News & Stories

News & Stories

Practical ideas, source-based analysis and original articles about software, AI and turning business needs into working systems.

News · Published 16 Oct 2026

China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers

Armory Castle exploited a BeyondTrust Remote Support zero-day on a self-hosted appliance and deployed the SAWFLY web shell.

The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026.

Source: The Hacker News — Read the original (opens in a new tab)

Read the story

News · Published 15 Oct 2026

Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

A critical Linux kernel flaw let a guest VM read host memory in Vercel's live sandboxes; host code execution was shown only in lab tests.

A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel's live cloud sandboxes, and Vercel confirmed it.

Source: The Hacker News — Read the original (opens in a new tab)

Read the story

News · Published 15 Oct 2026

Meta unveils Muse Spark Open, the new top U.S. open weights model — and it runs on two paired Mac desktops

Meta’s published results make Spark Open a contender with specific strengths, rather than an overall open-weight leader. Its model card reports an Artificial Analysis Intelligence Index score of 39, below MiMo-V2.6-Pro’

Chinese labs have become a go-to source for AI models businesses can download, customize and run on their own infrastructure. Alibaba’s Qwen, DeepSeek and Moonshot AI’s Kimi help set the competitive standard for open-weight systems, giving developers alternatives to proprietary models accessed through commercial APIs.

Read the story

News · Published 15 Oct 2026

Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing

Next.js patches two critical RCE flaws involving typed arrays and SVG processing, plus a Server Actions DoS affecting App Router apps.

Next.js released an out-of-band security update on October 14 that fixes two critical flaws allowing unauthenticated remote code execution, along with a high-severity denial-of-service flaw.

Source: The Hacker News — Read the original (opens in a new tab)

Read the story

News · Published 14 Oct 2026

CISA warns admins to immediately fix Ivanti flaw exploited as zero-day

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st.

Source: BleepingComputer — Read the original (opens in a new tab)

Read the story

News · Published 14 Oct 2026

Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days

XBOW built an AI-assisted, three-bug Chrome exploit chain in six days that enabled Windows code execution; Google has fixed all three bugs.

A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said.

Source: The Hacker News — Read the original (opens in a new tab)

Read the story

Original articles · Authored 14 Oct 2026

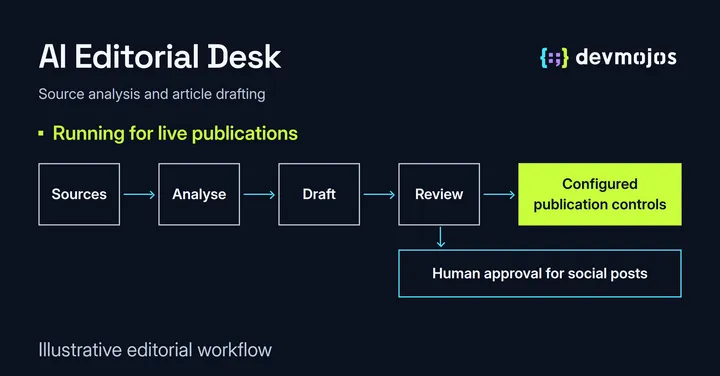
Give an AI workflow one useful job

Turn an approved brief and source material into a CMS draft an editor can review. Assess the workflow’s quality, human effort and cost.

A useful first AI workflow can have a recognisable job: turn an approved brief and source pack into a CMS draft that an editor can review. The task has an input, an intended result and a person who decides what happens next. Those boundaries give a focused pilot something concrete to evaluate.

Written with AI · Devmojos

Read the story

Original articles · Authored 14 Oct 2026

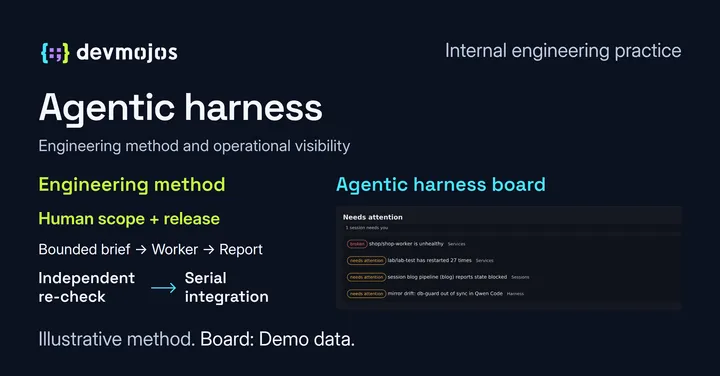
Experienced engineering, with AI in the delivery method

Business understanding, architecture, automated tests and independent review guide AI execution and human release decisions.

AI changes how implementation work can be carried out. Understanding a client’s business, users and systems remains central to deciding what to build. At Devmojos, the current delivery method connects that understanding with UX, architecture, defined AI tasks, testing and human decisions from discovery through release and ongoing improvement.

Written with AI · Devmojos

Read the story

News · Published 14 Oct 2026

AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host

Linux's Vghost flaw lets users with vhost device access gain root and, in specific VM setups, lets guests hijack host QEMU.

A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted virtual machine write to the host's memory and hijack the program that runs the virtual machine.

Source: The Hacker News — Read the original (opens in a new tab)

Read the story

News · Published 13 Oct 2026

Ghostscript flaw lets hackers hijack servers via PDF uploads

A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files.

A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files.

Source: BleepingComputer — Read the original (opens in a new tab)

Read the story

News · Published 13 Oct 2026

Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets

Anthropic warns small AI models could form IoT botnets; GLM-5.2 propagated Llama3.1-8B to eight nodes in four of five tests.

Small artificial intelligence (AI) models may be months away from developing capabilities to self-replicate on IoT devices like smart ovens and off-brand Android TV boxes, according to a warning from Anthropic.

Source: The Hacker News — Read the original (opens in a new tab)

Read the story

News · Published 13 Oct 2026

Sandbox vulnerability gives rogue AI agents a path to escape and leak data, research says

The new research, published by AI security startup AIR, found that a network filtering flaw in Vercel Sandbox — a tool used to run code in isolated environments — could allow agents to exploit certificate validation processes to transmit data outside approved networks.

Cybersecurity researchers on Monday said they discovered a vulnerability in a widely used AI development sandbox that could allow rogue agents to leak sensitive information by bypassing restrictions designed to keep them isolated.

Read the story

News · Published 13 Oct 2026

GitHub Tightens npm Publishing After Flaw Left 1,500+ Packages Vulnerable to Hijacking

GitHub now expires unvalidated npm trusted publisher bindings after 48 hours to limit package hijacks through reclaimed repository names.

GitHub has taken the step of expiring unvalidated npm trusted publishing configurations 48 hours after creation after researchers found that it was possible for an attacker to push new versions of a different user's package without having to steal their credentials.

Source: The Hacker News — Read the original (opens in a new tab)

Read the story

News · Published 13 Oct 2026

Google makes Gemini 4 Argon broadly available with limited-time low API pricing of $2/$10 per 1M token

The Gemini app gains more agentic functionality, including persistent tasks that can continue while users are away from their computers and connections to more than 40 external applications.

Google is making its new, flagship Gemini 4 Argon multimodal language AI model broadly available today, October 13.

Read the story